Open source technology offers electronics developers a way to reduce costs, accelerate time to market, and extend product lifecycles by removing proprietary barriers and fostering collaboration. Today, open source opportunities span the entire systems stack, from operating systems to single-board computer (SBC) hardware and semiconductor IP.
However, high computational requirements, security risks, and deterministic latency challenges remain a problem for running Linux on resource-constrained devices, such as industrial IoT (IIoT) and robotics systems.
This article briefly reviews the challenges designers face when implementing Linux on resource-constrained systems. It then introduces the BeagleBoard.org BeagleV-Fire single-board computer (SBC) in combination with Linux and describes how it can maximize future design flexibility. A demonstration of how to use Microchip Technology's open-source Board Support Packages (BSPs) to create an initial Linux configuration is included.
The challenges of open source development in embedded systems
The adoption of open-source technologies in embedded development is well established. Both hardware design and software integration are accelerated by the off-the-shelf assets produced by a broad ecosystem of individual manufacturers and engineers. In particular, Linux's flexibility has made it a leading software solution for systems requiring networking, high-level application frameworks, and artificial intelligence (AI) integration.
However, deploying Linux on devices with more resources introduces additional considerations:
- Computational demands: Traditional microcontroller units (MCUs) struggle to meet the memory and storage requirements of even minimal Linux distributions. As developers add background services to support user-space applications, subsystems, and frameworks (USFs), these subsystems consume more resources, making large software stacks impractical.
- Latency: High-precision applications, such as robotics and industrial automation, demand predictable timing for system coordination and operational safety. While the Linux kernel's PREEMPT_RT feature improves determinism, dedicated real-time operating systems (RTOS) offer lower latency and overhead for resource-constrained hardware.
- Security: Embedded systems deployed in public environments are at risk of unauthorized access, so standard security measures such as secure boot, tamper resistance, and hardware Root of Trust (RoT) are essential. Furthermore, regulations such as the EU Cyber Resilience Act (CRA) require products with digital components to be secure by design.
- Energy: Edge devices typically operate in remote environments with limited energy resources. Greater energy efficiency can extend battery life or enable operation using ambient power sources. Similarly, greater energy efficiency can simplify thermal management and increase performance per watt, supporting advanced edge processing.
- Lifecycle management: The CRA requires that digital devices receive support for at least five years, although many industrial deployments require 10 to 15 years of product availability. Therefore, to ensure ongoing compatibility with the Linux kernel, developers must plan for upgradeability and hardware availability.
To overcome these challenges, developers can draw on additional resources from open-source and embedded Linux ecosystems and leverage Linux's simplified hardware and software combinations for rapidly evolving edge applications.
Linux implementation using open SBCs and RISC-V
While general-purpose Linux distributions provide a fast track to application development, they often include packages and services that aren't necessary for the project at hand. In contrast, the Yocto Project, powered by OpenEmbedded, allows developers to create custom Linux images tailored to specific use cases. This eliminates unnecessary features, enabling lightweight distributions to run on resource-constrained hardware while retaining advanced capabilities such as AI-powered computer vision or predictive maintenance using standard tools.
In addition, the Yocto Project provides developers with:
- Reproducible constructions for long-term maintenance
- Custom core configuration to improve performance, security, and responsiveness
- Integration of specific board layers to ensure hardware-software compatibility and reduce development time
Easy integration with over-the-air (OTA) update mechanisms like SWUpdate, RAUC, and Mender also helps developers regularly improve device performance and security throughout the long product lifecycles. As a result, the Yocto Project is now a standard for embedded Linux systems.
Similarly, open-source SBCs have long been used to accelerate Linux application development, as they provide a ready-to-use reference platform that combines processing, memory, storage, and I/O resources in a self-contained form factor. With open SBCs, developers can quickly prototype a system, validate their software stack, and then transition to custom hardware with minimal rework.
The open-standard RISC-V instruction set architecture (ISA) takes this a step further by allowing system designers to create custom processing platforms without costly licensing fees. With RISC-V, designers can choose which parts of the instruction set to include and even extend them to meet their specific use cases. Because the original designs were created under a Berkeley Software Distribution (BSD) license, derivative works can be either open and free or closed and proprietary.
For developers and architects, the Yocto Project, open SBCs, and RISC-V reduce reliance on single-vendor roadmaps, increasing long-term design flexibility. Furthermore, the growing upstream support for RISC-V in Linux and Yocto Project's RISC-V Platinum membership underscore the embedded Linux community's interest.
A high-performance RISC-V SBC for compact Linux integration
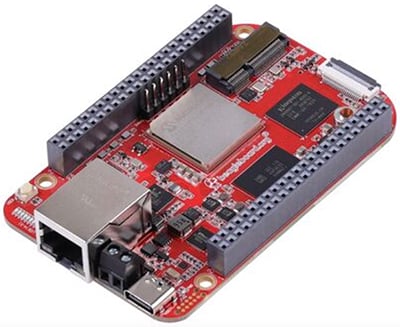
The open-source BeagleV-Fire SBC from BeagleBoard.org (Figure 1) offers a compact, I/O-rich platform to address these challenges. Featuring a Microchip PolarFire FPGA system-on-a-chip (SoC), it delivers low-power operation, hardware security features, and a coherent RISC-V CPU cluster that supports Linux applications running real-time workloads. Developers can use the SBC to prototype robotic controllers, industrial gateways, edge-AI accelerators, and custom I/O platforms based on embedded Linux.
The compact platform measures 86.38 mm × 54.61 mm × 18.8 mm and is built around the low-power PolarFire MPFS025T-FCVG484E SoC. It features a coherent multi-core architecture with four RV64GC application cores for running Linux and an RV64IMAC monitoring core for managing low-level functions.
To maximize performance and ensure data accuracy across all cores, the PolarFire SoC provides a shared L2 cache, a coherent memory subsystem, and an integrated DDR memory controller to support 2 gigabytes (GB) of onboard LPDDR4 memory. Complex applications are further supported by the BeagleV-Fire's 16 GB eMMC storage and 128 megabits (Mbit) of SPI flash memory.
Alongside the RISC-V processor subsystem, the PolarFire SoC integrates an FPGA fabric (Figure 2) that allows developers to build deterministic processing paths for low-latency, real-time applications and implement custom hardware acceleration for AI inference paths. As part of the complete system, this fabric houses 23 logic elements and its own supplementary resources, enabling it to operate independently of the main processing cores.
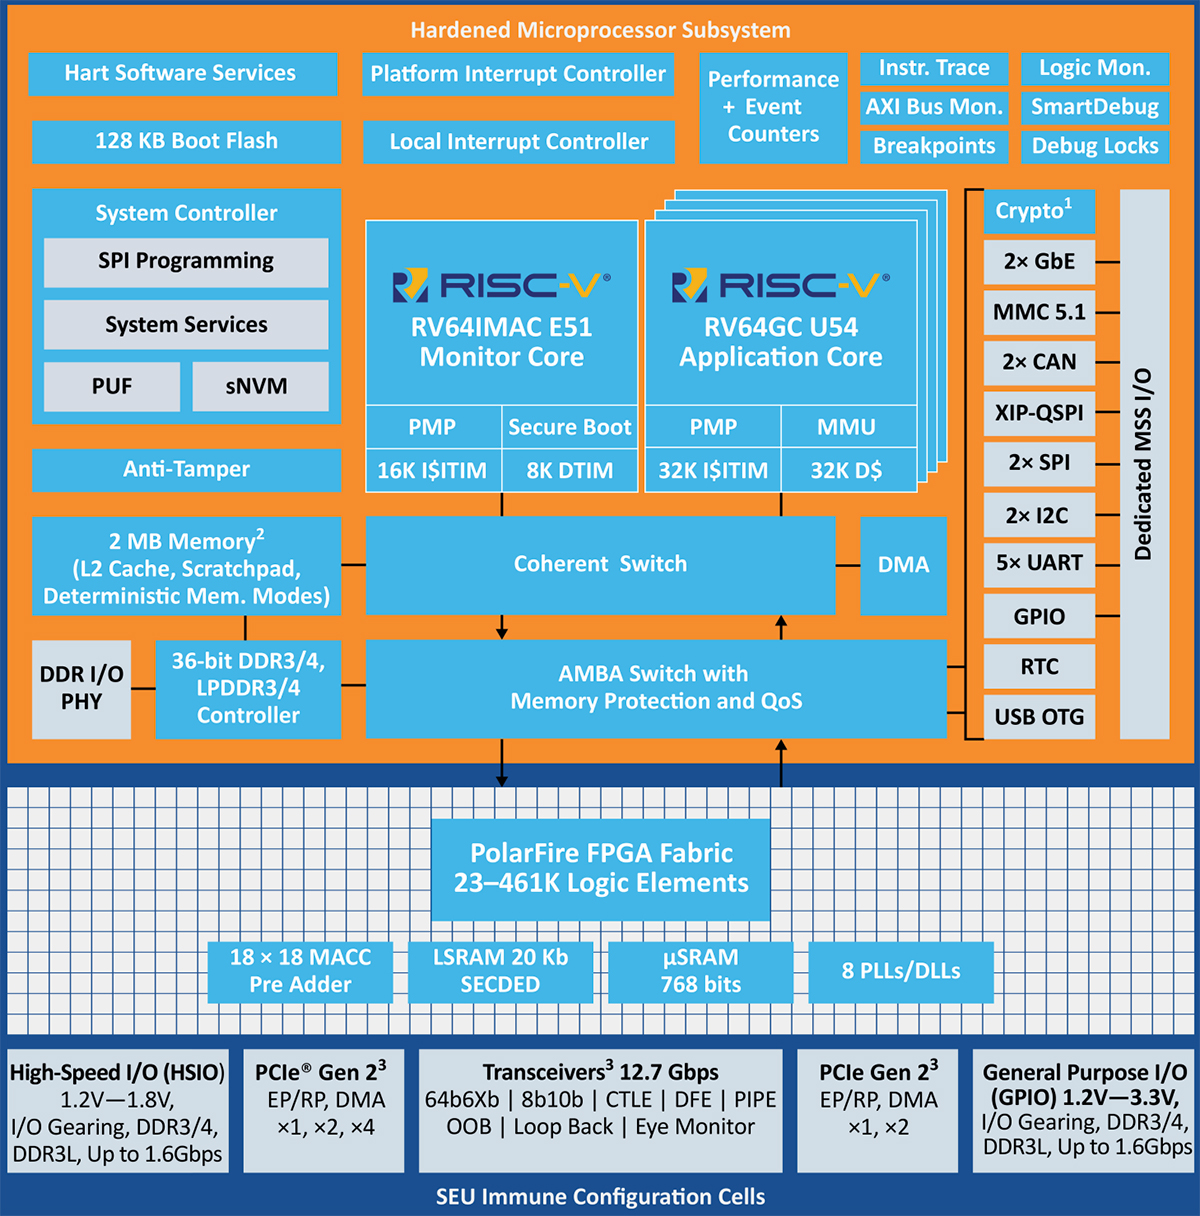 Figure 2. Microchip's PolarFire SoC family combines multiple RISC-V processing cores with a versatile FPGA fabric for deterministic workloads. (Image source: Microchip Technology)
With multiple secure boot options, the hardware security features built into the PolarFire SoC allow developers to implement a deep security model, making it a useful platform for meeting modern cybersecurity requirements. These features include:
- Immutable hardware root of trust through a physically non-clonable function (PUF)
- Secure key storage with one-time programming (OTP) or secure non-volatile storage using Unique Device Secrets (UDS) and hardware-enforced key access control.
- An anti-sabotage module
Beyond this, the BeagleV-Fire offers several integrated physical ports for building an application-ready system on which to verify and test custom Linux distributions (Figure 3). These include a Gigabit Ethernet RJ45 port, a USB Type-C port for power and connectivity, an M.2 Key E socket, two 46-pin BeagleBone-compatible Cape headers for further ecosystem expansion, and a Camera Serial Interface (CSI) for direct integration. A TAG-CONNECT JTAG footprint is provided for debugging, and the BeagleV-Fire also supports SYZYGY-compatible expansion for FPGA-oriented peripherals.
 Figure 3. Despite its small size, the BeagleV-Fire from BeagleBoard.org offers several physical ports for immediate application interconnection. (Image source: BeagleBoard.org)
How to build an initial Linux configuration on the BeagleV-Fire SBC
When building a lightweight Linux distribution for the BeagleV-Fire, developers must first obtain a suitable BSP layer from the Yocto Project. This will provide the U-Boot configuration, the default Linux kernel configuration, the device trees to support the board, and the peripheral support definitions. A GitHub repository supports all the BSPs from the PolarFire SoC evaluation kit, including the BeagleV-Fire.
After installing all the necessary Yocto Project dependencies, the following layers provide the foundation for the build and should be cloned:
- bitbake
- meta-openembedded-core
- meta-yocto (for the Poky reference distribution)
- meta-mchp-common
- meta-mchp-polarfire-soc/meta-mchp-polarfire-soc-bsp
- meta-mchp-polarfire-soc/meta-mchp-polarfire-soc-community
- Additional layers as required by the project
Once this is done, a minimal image can be built using the MACHINE target = "beaglev-fire" and a kas configuration file. Listing 1 shows an example configuration:
Copy
header:
  version: 19

repos:
  openembedded-core:
    url: git://git.openembedded.org/openembedded-core.git
    # yocto-5.0.15
    commit: 6988157ad983978ffd6b12bcefedd4deaffdbbd1
    layers:
      meta:

  bitbake:
    url: git://git.openembedded.org/bitbake.git
    # yocto-5.0.15
    commit: 8dcf084522b9c66a6639b5f117f554fde9b6b45a
    layers:
      bitbake: disabled

  meta-yocto:
    url: git://git.yoctoproject.org/git/meta-yocto.git
    # yocto-5.0.15
    commit: 9bb6e6e8b016a0c9dfe290369a6ed91ef4020535
    layers:
      meta-poky:
      meta-yocto-bsp:

  meta-mchp:
    url: https://github.com/linux4microchip/meta-mchp.git
    branch: scarthgap
    path: layers/third-party/meta-mchp
    layers:
      meta-mchp-common:
      meta-mchp-polarfire-soc/meta-mchp-polarfire-soc-bsp:
      meta-mchp-polarfire-soc/meta-mchp-polarfire-soc-community:

machine: beaglev-fire


local_conf_header:
  Users: |
    EXTRA_IMAGE_FEATURES = "allow-empty-password empty-root-password \
allow-root-login"
Listing 1. Shown is a sample configuration file that creates all the necessary build artifacts to boot the BeagleV-Fire into a simple shell. (Listing source: Microchip Technology)
Running "kas build core-image-minimal" will then create all the necessary compilation artifacts to boot the BeagleV-Fire into a simple shell, including the U-Boot binaries and a FIT image containing the Linux kernel and modules, the device tree, and the root filesystem.
Once a minimal Linux image for the BeagleV-Fire has been created using the Yocto Project, standard procedures can be followed to create a custom image and tailor the build to the exact project requirements. In robotics and industrial systems, for example, Linux is often used alongside a more traditional RTOS, such as FreeRTOS or Zephyr, to enable advanced processing alongside time-critical operations. This functionality is well supported by the BeagleV-Fire's PolarFire SoC, which can be configured to run multiple bare-metal operating systems or applications simultaneously.
Given that many embedded devices require a lifespan of 10 years or more, the combination of the open RISC-V ISA, Linux, and Yocto-based reproducibility allows PolarFire SoC-based platforms to adapt to emerging security threats and new application requirements through regular local or OTA updates. In this way, the BeagleV-Fire SBC provides an excellent starting point for open source adoption, boosting the flexibility and longevity of intelligent edge systems.
Conclusion
Computational limitations, deterministic latency requirements, security exposure, and long lifecycle demands can pose legitimate challenges when running Linux on resource-constrained embedded systems. The BeagleV-Fire SBC from BeagleBoard.org provides a hybrid architecture that combines the capabilities of RISC-V Linux with FPGA-based deterministic logic and hardware security features to overcome these challenges. When combined with the Yocto Project and Microchip's open-source BSP layers, developers can use this platform to create custom, traceable Linux distributions optimized for long-life robotics, IIoT, and edge computing applications.
Source: Digikey